

North Carolina A&T Condition College, the biggest traditionally black university in the US, College was not too long ago struck by a ransomware Group called ALPHV, sending university personnel into a scramble to restore companies final month.
“It’s affecting a ton of my classes, in particular due to the fact I do get a pair of coding lessons, my lessons have been canceled,” Melanie McLellan, an industrial system engineering university student, told the faculty newspaper, The A&T Sign-up. “They have been remote, I nevertheless haven’t been in a position to do my assignments.”
The paper explained the breach transpired the week of March 7 when learners and faculty were on spring crack. Devices taken down by the intrusion integrated wi-fi connections, Blackboard instruction, single signal-on internet sites, VPN, Jabber, Qualtrics, Banner Doc Administration, and Chrome River, several of which remained down when the scholar newspaper revealed its tale two weeks back.
The report came a working day following North Carolina A&T appeared on a darknet site that ALPHV takes advantage of to identify and shame victims in an attempt to persuade them to pay out a hefty ransom.
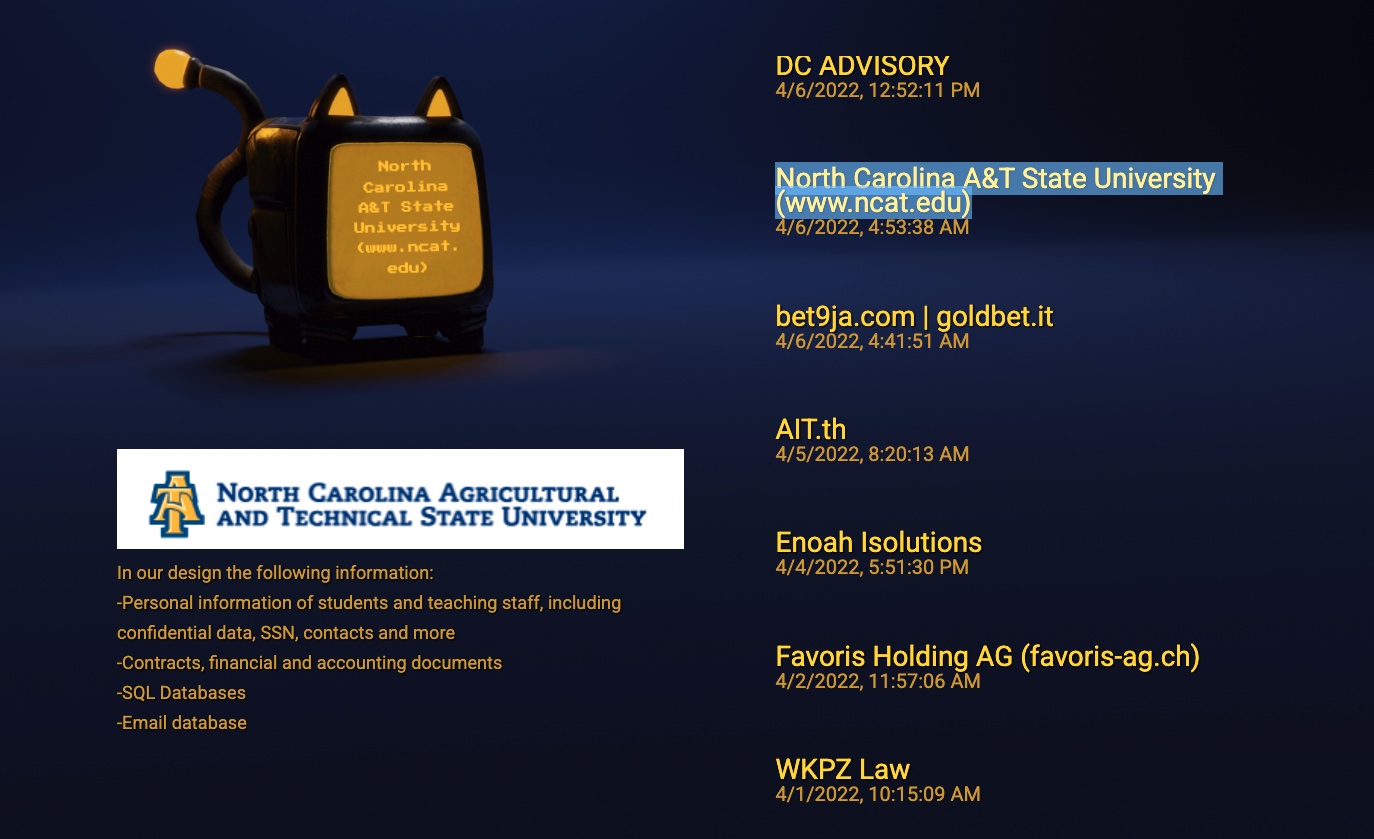
ALPHV, which also goes by the identify Black Cat, is a relative newcomer to the ransomware-as-a-provider scene, in which a core group of developers functions with affiliate marketers to infect victims and then split any proceeds that final result. Some of its associates have portrayed ALPHV as a successor to the BlackMatter and REvil ransomware groups, and on Thursday, scientists at protection organization Kaspersky presented proof that backed up that assert.
Brazen code reuse
An exfiltration resource earlier utilized completely by BlackMatter, Kaspersky explained, is being employed by ALPHV/Black Cat and “represents a new info stage connecting BlackCat with earlier BlackMatter action.” Earlier, BlackMatter employed the so-referred to as Fendr instrument to obtain info prior to encrypting it on the victim’s server. The exfiltration supports a double extortion model that necessitates a payment not just for a decryption essential but also for a pinky swear that criminals will not make the knowledge general public.
“In the earlier, BlackMatter prioritized selection of sensitive information and facts with Fendr to properly support their double coercion plan, just as BlackCat is now doing, and it demonstrates a sensible but brazen example of malware re-use to execute their multi-layered blackmail,” Kaspersky researchers wrote. “The modification of this reused software demonstrates a extra complex arranging and growth program for adapting prerequisites to target environments, characteristic of a more productive and experienced criminal plan.”
Kaspersky claimed the ALPHV ransomware is strange due to the fact it’s prepared in the Rust programming language. Another oddity: The unique ransomware executable is compiled exclusively for the group staying focused, frequently just several hours right before the intrusion, so that beforehand collected login credentials are hardcoded into the binary.
Thursday’s article explained Kaspersky scientists had noticed two AlPHV breaches, a person on a cloud hosting service provider in the Center East and the other versus an oil, gasoline, mining, and construction business in South The us. It was throughout the 2nd incident that Kaspersky detected the use of Fendr. Other breaches attributed to ALPHV incorporate two German oil suppliers and luxury fashion brand name Moncler.
A&T is the seventh US college or faculty to be strike by ransomware so far this yr, according to Brett Callow, a security analyst at safety firm Emsisoft. Callow also mentioned that at the very least eight university districts have also been strike, disrupting functions at as many as 214 schools.